Founder · Networking
Atul Sharma
12+ years in networkingNetworking experience spanning Aricent, TCS, Apple and Juniper.
Join Splunk Certification Training to learn data analysis & monitoring. Get practical training to working on live projects & boost your data analytics career.
We also provide certification after you complete the course. Pass a proctored Network Kings assessment and receive a certificate with a unique credential ID and a public verification record. Students can check it in seconds, and no login is needed.
Prepare, take your assessment, and share your achievement.
Select Get Certification on your course in the Network Kings learning app.
Answer the timed questions in one sitting with your camera on and the exam in fullscreen.
The certification team reviews your result and emails your certificate within 24 hours.
Add it to LinkedIn or your CV. Anyone can confirm it with the ID or QR code.
The Splunk program helps individuals gain expertise in using Splunk, a powerful platform for monitoring, searching, analyzing, and visualizing machine-generated big data. Splunk is widely used in fields like cybersecurity, IT operations, data analytics, and business intelligence. The program covers topics such as-
Explore each area of the curriculum and the topics covered.
Are you looking to advance your daily management of Splunk Enterprise as a certified admin? Then, you are at the right place. Stand out from your peers by taking the Splunk course. Learn how to configure, monitor, and get data in with the help of real-time industry engineers. Become a vigilant strategist by gaining valuable insights into the business data. Learn how to make strategic business decisions using data by enrolling in the Splunk course by Network Kings. Do not miss the chance to learn directly from IT engineers with over 12 years of industry experience.
The scope of the Splunk training is quite vast and promising. It is discussed below:
Network Kings is a one-stop solution to gaining hands-on skills using the Splunk software, where you can learn directly from top-notch IT engineers with over 12 years of industry experience. The advantages of enrolling at Network Kings for Splunk training are mentioned below-
There are various job opportunities available after completing the Splunk training.
Splunk Enterprise Certified Administrator is stage 6 of 6 in the Network Kings Cyber Security Learning Path. Learners usually complete CISSP first. It is the final stage of the roadmap.
See the full Cyber Security roadmap Explore more career roadmaps
Move from understanding a system to configuring, testing and improving it through guided practice.
Trace connections and practice working with devices and services.
Explore lab scenarios and inspect how configuration choices affect a system.
Explore Linux, scripting and automation in the relevant learning paths.
Confirm the available labs and access period for your chosen course.
Meet instructors who bring networking, cloud and automation experience into the classroom.
Networking experience spanning Aricent, TCS, Apple and Juniper.
Cloud mentor bringing extensive hands-on AWS experience to the classroom.
DevOps automation experience at CDAC, IBM and Integrated Solutions.
Industry experience. Practical explanations. A human connection.
Explore Network Kings
Network L1
Shared with Network Kings“Always thankful to Network Kings for their guidance and support.”
Network Engineer L1
Shared with Network Kings“Industry-expert trainers made networking easy to understand.”
See the syllabus and fees at your own pace. Request personal guidance when you need help choosing.
Use the enquiry form to share your course interest, or WhatsApp/email to include a callback or guidance request.
CCIE Security training certification deals with the study of complex Security Solutions and further helps in understanding, designing, read more.
Prepare for CCNP Security certification with expert-led training, hands-on labs, and practical network security skills. Start your CCNP Security course today.
Explore ethical hacking in authorized lab environments, including reconnaissance, vulnerability assessment, application security, and reporting.
Because passing an exam and doing the job are different skills, and only experience closes the gap. Network Kings mentors have spent 11 to 20+ years building and running networks, cloud platforms and pipelines at companies like Apple, Juniper Networks, IBM and CDAC. They teach what breaks in production, why, and how engineers fix it under pressure.
 Atul Sharma, Founder & CEO
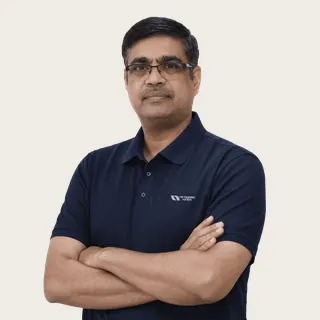 Sanjay Sharma, AWS
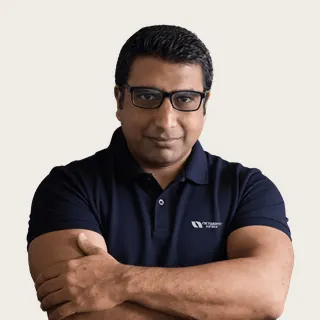 Vikas Kumar, Azure
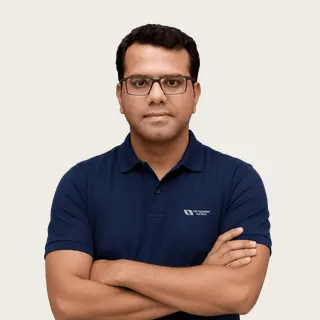 Ajay, Azure
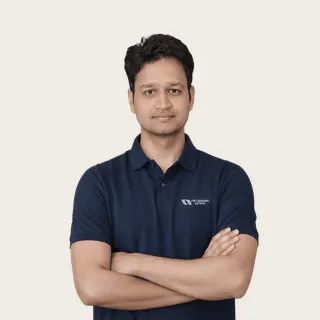 Amit Bhatt, Linux & DevOps
 Lazaro (Laz) Diaz, Networking
Atul Sharma (Founder & CEO, 12+ yrs), Sanjay Sharma (AWS, 20+ yrs), Vikas Kumar (Azure, 20+ yrs) and more. Meet the mentors
Same problem, two answers. Pick a track:
On the job: The SIEM raises hundreds of alerts before lunch, and one of them is real.
A SIEM collects logs and generates alerts. Analysts investigate each alert and escalate incidents.
Correct. Not enough to fix it.