Diwali Mega SaleIT 360 Bundle free with every master programGrab the offer
Cybersecurity

CompTIA PenTest+ Course

CompTIA PenTest+ is a certification for cybersecurity professionals tasked with penetration testing and vulnerability assessment and management.
Planning and ScopingInformation gathering and Vulnerability ScanningAttack and Exploits
Need help choosing? Request career guidance
Concept illustration of an authorized security-testing lab with assessment targets and evidence.
CompTIA PenTest+ Course — conceptual illustration

Finish CompTIA PenTest+. Earn a certificate students can verify

We also provide certification after you complete the course. Pass a proctored Network Kings assessment and receive a certificate with a unique credential ID and a public verification record. Students can check it in seconds, and no login is needed.
  • Issued by Network Kings. The record comes from our system and can’t be edited by the holder.
  • Live status. If a certificate is ever revoked, its record says so immediately.
  • Score on record. The assessment score is shown, so the result speaks for itself.
NETWORK KINGS - Official Digital Credential
Sample credential
Priya Menon
CompTIA PenTest+ Certification Assessment
Credential ID
Issued
NK-CERT-2026-104729
14 Aug 2026
Sample credential. Real credentials link to a live verification record.

How to get certified

Prepare, take your assessment, and share your achievement.

  1. Open the exam from your course

    Select Get Certification on your course in the Network Kings learning app.

  2. Take the proctored assessment

    Answer the timed questions in one sitting with your camera on and the exam in fullscreen.

  3. Pass with 70% or more

    The certification team reviews your result and emails your certificate within 24 hours.

  4. Share it anywhere

    Add it to LinkedIn or your CV. Anyone can confirm it with the ID or QR code.

THE COURSE AT A GLANCE

About this course

The CompTIA PenTest+ Certification course provides the skills required to plan, scan, and perform vulnerability and penetration testing as it is both, a knowledge-based and performance-based PenTest+ exam. Since the PenTest+ course refers to the practice of testing a computer system, network or web application in finding security vulnerabilities which can be damaged by malicious cyber attacks, CompTIA PenTest+ training covers the security of all the technologies. It is the only exam available till date which covers all the vulnerability management requirements. The exam includes cloud, hybrid environment, web applications, Internet of Things (IoT), and traditional on-premises testing skills.

Skills you’ll develop

  • Planning and Scoping
  • Information Gathering and Vulnerability Scanning
  • Attacks and Exploits
  • Reporting and Communication
  • Tools and Code Analysis
  • What is the CompTIA PenTest+ Program?
  • Why is CompTIA PenTest+ Training Required?
  • Job Opportunities After CompTIA PenTest+ Certification
EXPLORE THE SYLLABUS

Built around the skills you need

Explore each area of the curriculum and the topics covered.

Planning and Scoping
  • Compare and contrast governance, risk, ad compliance concepts
  • Explain the importance of scoping organizations/customer requirements
  • Given a scenario, demonstrate an ethical hacking mindset by maintaining professionalism and integrity.
Information gathering and Vulnerability Scanning
  • Given a scenario, perform passive reconnaissance
  • Given a scenario, perform active reconnaissance
  • Given a scenario, analyze the results of a reconnaissance exercise
  • Given a scenario, perform vulnerability scanning
Attack and Exploits
  • Given a scenario, research attack vectors and perform network attacks
  • Given a scenario, research attack vectors and perform wireless attacks
  • Given a scenario, research attack vectors and perform application-based attacks
  • Given a scenario, research attack vectors and perform attacks on cloud technologies
  • Explain common attacks and vulnerabilities against specialized systems
  • Given a scenario, perform a social engineering or physical attack
  • Given a scenario, perform post-exploitation techniques.
Reporting and Communication
  • Compare and contrast important components of written reports
  • Given a scenario, analyze the findings and recommend the appropriate remediation within a report
  • Explain the importance of communication during the penetration testing process
  • Explain post-report delivery activities
Tools and Code Analysis
  • Explain the basic concepts of scripting and software development
  • Given a scenario, analyze a script or code sample for use in a penetration test
  • Explain the use cases of the following tools during the phases of a penetration test.
GO DEEPER

More about this course

Eligibility
  • Graduation
  • Basic understanding of the IT industry
  • Basic understanding of Networking
  • Understanding Security fundamentals
  • 3-4 years of experience in IT Security
Everything You Need to Know About the Online CompTIA PenTest+ Course

Are you looking for the best CompTIA PenTest+ training in IT? Look no further! Here we are with the top-notch CompTIA PenTest+ certification course for you to excel in the tech world.

To break into the cybersecurity industry as a Penetration Tester, CompTIA PenTest+ is the best certification. It proves your hands-on skills in penetration testing and vulnerability management.

NOTE: You can kickstart your career with the guidance of top-notch Network Engineers with the CompTIA PenTest+ course training.

What is the CompTIA PenTest+ program?

The CompTIA PenTest+ certification course helps to build a career in vulnerability management and penetration testing. CompTIA PenTest+ is the best cybersecurity certification to enter the world of penetration testing as it tests your ability hands-on along with performance-based questions. With the CompTIA PenTest+ course, you can learn management skills to plan, predict, and manage weaknesses.

Why is the CompTIA PenTest Training required?

After you get the CompTIA PenTest+ training, you end up learning the following skills-

  • Plan and measure risk and compliance concepts to defend against cyberattacks
  • Report and communicate in a regulatory environment during the pen testing process.
  • Perform vulnerability scanning, vulnerability management, and information gathering
  • Analyze a script or code sample and understand the use cases of various tools during the phases of penetration testing
  • Expand attack surfaces and perform network attacks and wireless attacks

After learning all these skills, you can find several job opportunities in the security industry. Getting a certification will increase your value in the industry. Therefore, getting CompTIA PenTest+ certified before entering the security industry is highly recommended.

How can you become CompTIA PenTest+ certified?

As if by October 2021, the CompTIA council has updated its exam from PT0-001 to PT0-002. This new exam covers the latest technologies and new methods to handle cybersecurity attacks.

Therefore, to earn the CompTIA PenTest+ certification, one must take the PT0-002 exam. The CompTIA PenTest+ PT0-002 exam covers the following topics-

  • Planning and Scoping
  • Information Gathering and Vulnerability Scanning
  • Attacks and Exploits
  • Reporting and Communication
  • Tools and Code Analysis

Once you cover all these domains, you are all set to take the CompTIA PenTest+ exam.

There are no harsh pre-requirements to earn the CompTIA PenTest+ certification. Yet, there are some recommended steps before you pursue the CompTIA PenTest+ course, such as-

  • Get CompTIA Network+ and CompTIA Security+ certified. Even an equivalent experience is also valid.
  • You also need at least 3-4 years of hands-on experience in Information Security or a related field.

If you have the following, you are ready to become CompTIA PenTest+ certified.

Is the CompTIA PenTest+ course worth it in IT?

The CompTIA PenTest+ certification is the only certification in the industry that covers all the aspects of vulnerability management. So, if you wish to get into penetration testing, you can take the CompTIA PenTest+ training.

It covers hands-on vulnerability assessment, scanning and monitoring and helps to plan, scope, analyze, and manage system weakness, which makes CompTIA PenTest+ the best certification in IT security to date.

Thus, the CompTIA PenTest+ course is utterly worth it!

Who is eligible to take the online CompTIA PenTest+ certification exam?

Anyone can take the CompTIA PenTest+ certification exam since there are no pre-requirements. However, there are some steps that you need to follow before taking the online CompTIA PenTest+ course exam.

The following before taking the CompTIA PenTest+ training:

  • CompTIA Network+ and CompTIA Security+ certification. An equivalent experience is also valid.
  • You need at least 3-4 years of experience in Information Security or a related field.
What next after earning the CompTIA PenTest+ course with certification?

After earning the CompTIA PenTest+ course certification, you can enroll in the following courses-

  • Certified Ethical Hacking (CEH v12) You can become a Certified Ethical Hacker to predict, strategize, and take action before any cyber attack.
  • Certified Information Systems Security Professional (CISSP) CISSP is an advanced-level cybersecurity professional certification for candidates wishing to become IT Security Analysts.

NOTE: After earning the CompTIA PenTest+ certification, you can explore various placement opportunities in the security industry.

What are the available job opportunities after CompTIA PenTest+ training certification?

You can explore various jobs after earning the CompTIA PenTest+ training certification, such as-

  1. Penetration Tester
  2. Ethical Hacker
  3. Security Consultant
  4. Security Analyst
  5. Vulnerability Assessor
  6. Cybersecurity Engineer
  7. Incident Response Analyst
  8. Information Security Manager
  9. Network Security Engineer
  10. Security Operations Center (SOC) Analyst
  11. Cybersecurity Specialist
  12. Security Architect
  13. Red Team Operator
  14. Blue Team Operator
  15. Cybersecurity Trainer/Instructor
  16. Forensic Analyst
  17. Risk Analyst
  18. Security Auditor
  19. Compliance Officer
  20. Cybersecurity Program Manager
YOUR CAREER ROADMAP

Where this course takes you

CompTIA PenTest+ Course is stage 3 of 6 in the Network Kings Cyber Security Learning Path. Learners usually complete CompTIA CySA+ first. The next step is CEH v13.

From Security+ foundations to CISSP expertise 6 stages · about 215 training hours
  1. Start before this

    CompTIA Security+

    35 hours · beginner

    • Threat management
    • Vulnerabilities
    • Incident response
  2. Start before this

    CompTIA CySA+

    30 hours · intermediate

    • Threat detection
    • Incident response
    • Security tools
  3. You are here

    CompTIA PenTest+

    30 hours · intermediate

    • Penetration testing
    • Vulnerability assessment
    • Reporting
  4. Next step

    CEH v13

    40 hours · intermediate

    • Ethical hacking
    • Reconnaissance
    • Web testing
  5. Next step

    CISSP

    50 hours · advanced

    • Security management
    • Risk
    • Architecture
  6. Next step

    Splunk SIEM

    30 hours · advanced

    • Log analysis
    • SIEM
    • Threat hunting
Ready to start with CompTIA PenTest+ Course?Try the free lab first, or review the fee and enroll in a few steps.

Connect the concepts.
Put them to work

Move from understanding a system to configuring, testing and improving it through guided practice.

  • Configure a network

    Trace connections and practice working with devices and services.

  • Test what changes

    Explore lab scenarios and inspect how configuration choices affect a system.

  • Build repeatable workflows

    Explore Linux, scripting and automation in the relevant learning paths.

Explore the lab environments

Confirm the available labs and access period for your chosen course.
Illustration of a miniature switch, servers, cloud, security gateway and delivery modules connected in an infrastructure learning lab.
A connected view of networking, cloud, security and automation.

Learn from top 1% engineers.

Meet instructors who bring networking, cloud and automation experience into the classroom.

Atul Sharma
Founder · Networking

Atul Sharma

12+ years in networking

Networking experience spanning Aricent, TCS, Apple and Juniper.
Sanjay Sharma
AWS cloud

Sanjay Sharma

20+ years of experience

Cloud mentor bringing extensive hands-on AWS experience to the classroom.
Amit Bhatt
Linux & DevOps

Amit Bhatt

11+ years of experience

DevOps automation experience at CDAC, IBM and Integrated Solutions.

Industry experience. Practical explanations. A human connection.

Explore Network Kings
Aadil Hameed dar

Aadil Hameed dar

Network Engineer L1

“Industry-expert trainers made networking easy to understand.”

Shared with Network Kings

Explore, talk it through, or enroll

See the syllabus and fees at your own pace. Request personal guidance when you need help choosing.

Find the right direction

Discuss your experience, interests and the skills you want to build with our team.

Request career guidance

Have a course question?

Ask about prerequisites, live classes, lab access or the enrollment options for your course.

Request a callback

Ready for your next skill?

Compare our learning formats, then open your chosen course to review enrollment options.

Explore learning plans

Use the enquiry form to share your course interest, or WhatsApp/email to include a callback or guidance request.

Why learn from the top 1% of engineers?

Because passing an exam and doing the job are different skills, and only experience closes the gap. Network Kings mentors have spent 11 to 20+ years building and running networks, cloud platforms and pipelines at companies like Apple, Juniper Networks, IBM and CDAC. They teach what breaks in production, why, and how engineers fix it under pressure.
  • Atul Sharma, Founder & CEO mentor at Network KingsAtul Sharma, Founder & CEO
  • Sanjay Sharma, AWS mentor at Network KingsSanjay Sharma, AWS
  • Vikas Kumar, Azure mentor at Network KingsVikas Kumar, Azure
  • Ajay, Azure mentor at Network KingsAjay, Azure
  • Amit Bhatt, Linux & DevOps mentor at Network KingsAmit Bhatt, Linux & DevOps
  • Lazaro (Laz) Diaz, Networking mentor at Network KingsLazaro (Laz) Diaz, Networking

Atul Sharma (Founder & CEO, 12+ yrs), Sanjay Sharma (AWS, 20+ yrs), Vikas Kumar (Azure, 20+ yrs) and more. Meet the mentors

Same problem, two answers. Pick a track:

On the job: The SIEM raises hundreds of alerts before lunch, and one of them is real.

The textbook answer

A SIEM collects logs and generates alerts. Analysts investigate each alert and escalate incidents.

Correct. Not enough to fix it.
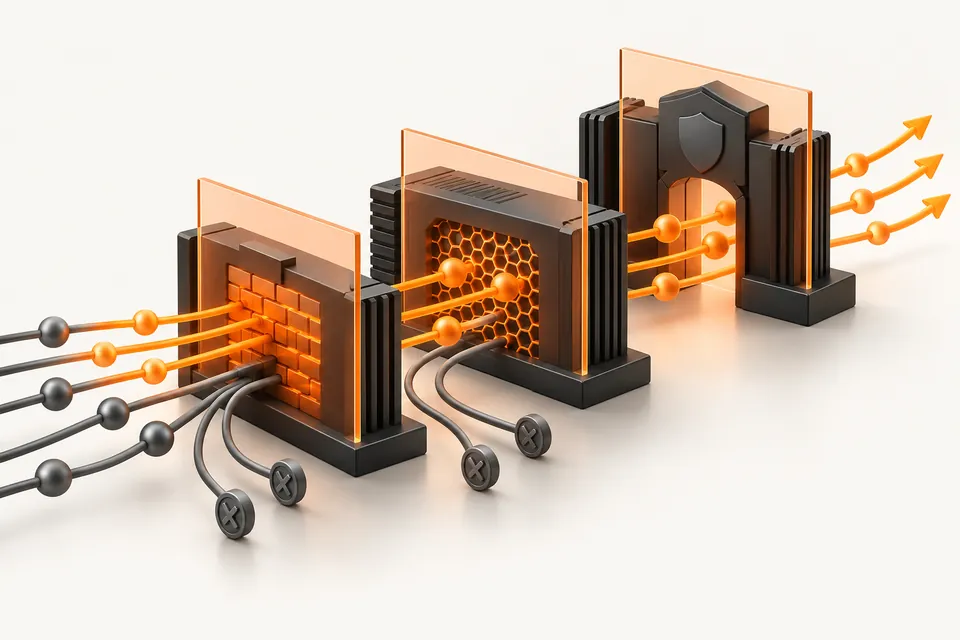
How a production engineer teaches it

  1. Triage by asset value and attack stage, not by arrival time.
  2. Join the login, the process tree and the outbound connection into one story.
  3. Contain the host, then hand over a timeline the incident team can act on.
  4. Tune the noisy rule so tomorrow's queue is shorter than today's.
  • The why behind every command, not just the syntax.
  • Hands-on labs for every topic, so the first fault you fix is not at work.
  • Doubts answered by someone who has fixed it in a live network, cloud or pipeline.