Diwali Career Utsav: Master programs + IT 360 Bundle free, 24×7 labs and a resume & career sessionExplore master programs
Cybersecurity

CISSP Training - Certified Information Systems Security Professional

Looking to upgrade your skills in IT? CISSP Training is the best way to learn how to protect and defend networks from cyber attacks.
Security and Risk ManagementAsset SecuritySecurity Architecture and Engineering
Need help choosing? Request career guidance
Concept illustration of identity, access and data protection fundamentals.
CISSP Training - Certified Information Systems Security Professional — conceptual illustration

Finish CISSP Training - Certified Information Systems Security Professional. Earn a certificate students can verify.

We also provide certification after you complete the course. Pass a proctored Network Kings assessment and receive a certificate with a unique credential ID and a public verification record. Students can check it in seconds, and no login is needed.
  • Issued by Network Kings. The record comes from our system and can’t be edited by the holder.
  • Live status. If a certificate is ever revoked, its record says so immediately.
  • Score on record. The assessment score is shown, so the result speaks for itself.
NETWORK KINGS - Official Digital Credential
Sample credential
Priya Menon
CISSP Training - Certified Information Systems Security Professional Certification Assessment
Credential ID
Issued
NK-CERT-2026-104729
14 Aug 2026
Sample credential. Real credentials link to a live verification record.

How to get certified

Prepare, take your assessment, and share your achievement.

  1. Open the exam from your course

    Select Get Certification on your course in the Network Kings learning app.

  2. Take the proctored assessment

    Answer the timed questions in one sitting with your camera on and the exam in fullscreen.

  3. Pass with 70% or more

    The certification team reviews your result and emails your certificate within 24 hours.

  4. Share it anywhere

    Add it to LinkedIn or your CV. Anyone can confirm it with the ID or QR code.

THE COURSE AT A GLANCE

About this course.

The CISSP training program comprises designing, implementing, and managing best-in-class cybersecurity programs. With a CISSP certification, one can validate the expertise and evolve as an (ISC)² member by opening an expansive exhibition of premier resources, scholarly devices, and peer-to-peer networking possibilities.

Skills you’ll develop.

  • Security and Risk Management
  • Asset Security
  • Security Architecture and Engineering
  • Communication and Network Security
  • Identity and Access Management (IAM)
  • Security Assessment and Testing
  • Security Operations
  • Software Development Security
EXPLORE THE SYLLABUS

Built around the skills you need.

Explore each area of the curriculum and the topics covered.

Security and Risk Management
  • Understand, adhere to, and promote professional ethics
  • Understand and apply security concepts
  • Evaluate and apply security governance principles
  • Determine compliance and other requirements
  • Understand legal and regulatory issues that pertain to information security in a holistic context
  • Understand requirements for investigation types (i.e., administrative, criminal, civil, regulatory, industry standards)
  • Develop, document, and implement security policy, standards, procedures, and guidelines
  • Identify, analyze, and prioritize Business Continuity (BC) requirements
  • Contribute to and enforce personnel security policies and procedures
  • Understand and apply risk management concepts
  • Understand and apply threat modelling concepts and methodologies
  • Apply Supply Chain Risk Management (SCRM) concepts
  • Establish and maintain a security awareness, education, and training program
Asset Security
  • Identify and classify information and assets
  • Establish information and asset handling requirements
  • Provision resources securely
  • Manage data lifecycle
  • Ensure appropriate asset retention (e.g., End-of-Life (EOL), End-of-Support (EOS))
  • Determine data security controls and compliance requirements.
Security Architecture and Engineering
  • Research, implement and manage engineering processes using secure design principles
  • Understand the fundamental concepts of security models (e.g., Biba, Star Model, Bell-LaPadula)
  • Select controls based upon systems security requirements
  • Understand security capabilities of Information Systems (IS) (e.g., memory protection, Trusted Platform Module (TPM), encryption/decryption)
  • Assess and mitigate the vulnerabilities of security architectures, designs, and solution elements
  • Select and determine cryptographic solutions
  • Understand methods of cryptanalytic attacks
  • Apply security principles to site and facility design
  • Design site and facility security controls.
Communication and Network Security
  • Assess and implement secure design principles in network architectures
  • Secure network components
  • Implement secure communication channels according to design.
Identity and Access Management (IAM)
  • Control physical and logical access to assets
  • Manage identification and authentication of people, devices, and services
  • Federated identity with a third-party service
  • Implement and manage authorization mechanisms
  • Manage the identity and access provisioning lifecycle.
Security Assessment and Testing
  • Design and validate assessment, test, and audit strategies Conduct security control testing
  • Collect security process data (e.g., technical and administrative)
  • Analyze test output and generate report
  • Conduct or facilitate security audits
Security Operations
  • Understand and comply with investigations
  • Conduct logging and monitoring activities
  • Perform Configuration Management (CM) (e.g., provisioning, baselining, automation)
  • Apply foundational security operations concepts
  • Apply resource protection
  • Conduct incident management
  • Operate and maintain detective and preventative measures
  • Implement and support patch and vulnerability management
  • Understand and participate in change management processes
  • Implement recovery strategies
  • Implement Disaster Recovery (DR) processes
  • Test Disaster Recovery Plans (DRP)
  • Participate in Business Continuity (BC) planning and exercises
  • Implement and manage physical security
  • Address personnel safety and security concerns.
Software Development Security
  • Understand and integrate security in the Software Development Life Cycle (SDLC)
  • Identify and apply security controls in software development ecosystems
  • Assess the effectiveness of software security
  • Assess security impact of acquired software
  • Define and apply secure coding guidelines and standards.
GO DEEPER

More about this course.

Eligibility
  • Graduation
  • Basic understanding of the IT industry
  • A minimum of 5 years of work experience
  • Any ISC2 approved course certification (Preferred)
  • 1-2 years of experience in developing and maintaining Cisco Applications
  • Fundamental knowledge of Programming Language
Everything You Need to Know About the Online CISSP Training

Are you looking for the best online CISSP training in IT? Look no further! Here we are with the top-notch CISSP certification course by experts to help you excel in the industry.

NOTE: You can also begin your online CISSP training by learning directly from cybersecurity experts!

What is CISSP?

CISSP is an advanced-level cybersecurity professional certification for candidates wishing to become IT Security Analysts. The CISSP certification is an acronym for Certified Information Systems Security Professional. The CISSP certification validates your skills in designing, implementing, and monitoring a cybersecurity program as an IT Security Analyst. The CISSP training opens a gateway to many job opportunities in the cybersecurity industry.

The best part about the CISSP online training at Network Kings is that we provide hands-on, practical training so that you become job-ready. We aim to produce the best cybersecurity professionals.

NOTE: The CISSP certification training is one of the most famous certification training among cybersecurity courses. You can begin your advanced cybersecurity journey with us!

What are the requirements to enroll in the CISSP course training?

CISSP course is an advanced-level cybersecurity course in IT. The eligibility criteria are well-regulated and demand more experience. To qualify to take the CISSP exam, you need to have five or more years of work experience in any two out of the eight cybersecurity domains, namely-

  • Security and Risk Management
  • Asset Security
  • Security Architecture and Engineering
  • Communication and Network Security
  • Identity and Access Management
  • Security Assessment and Testing
  • Security Operations
  • Software Development Security.

Having hands-on experience in any of the above two domains to appear for the CISSP exam is mandatory.

Here is the good news:

  • If you have a four-year graduate degree in Computer Science or BTech in CSE, you can compensate for one year of experience required for the CISSP certification.
  • You can also give the exam before having any hands-on experience. You can complete the six years of experience after clearing the exam.

The CISSP training is the best for those interested in expanding their knowledge of diverse security practices and principles in IT.

How to earn the CISSP certification in IT?

You can get CISSP course training from Network Kings to become the most in-demand cybersecurity professional in the industry. Formulated by the International Information Systems Security Certification Consortium (ISC), the CISSP certification is the most sought-after certification among all other cybersecurity certification courses.

Is the CISSP training worth it in IT?

The CISSP course validates skills for high-level cybersecurity professionals seeking to work in auditing and management. Therefore, the CISSP certification is the best cybersecurity certification to upskill in IT, which is a cutting-edge sign that the CISSP certification is worth it. Anyone having over 5+ years of experience in the industry can take the CISSP exam.

What domains are there in the CISSP training?

The following eight CISSP domains are in the CISSP syllabus-

  • Security and Risk Management
  • Asset Security
  • Security Architecture and Engineering
  • Communication and Network Security
  • Security Assessment and Testing
  • Identity and Access Management (IAM)
  • Security Operations
  • Software Development Security

What are you waiting for? Enroll now in our CISSP online training program.

What are the job roles after the CISSP certification course?

The top available job roles after the CISSP certification course are as follows-

  1. Security Analyst
  2. Information Security Manager
  3. Network Security Engineer
  4. Security Consultant
  5. Penetration Tester
  6. Security Architect
  7. Cybersecurity Manager
  8. IT Security Administrator
  9. Security Systems Engineer
  10. Risk Management Analyst
  11. Incident Response Analyst
  12. Security Auditor
  13. Chief Information Security Officer (CISO)
  14. Security Operations Center (SOC) Analyst
  15. Cybersecurity Consultant
  16. Compliance Officer
  17. Security Trainer
  18. Security Software Developer
  19. Malware Analyst
  20. Ethical Hacker
YOUR CAREER ROADMAP

Where this course takes you.

CISSP Training - Certified Information Systems Security Professional is stage 5 of 6 in the Network Kings Cyber Security Learning Path. Learners usually complete CEH v13 first. The next step is Splunk SIEM.

From Security+ foundations to CISSP expertise 6 stages · about 215 training hours
  1. Start before this

    CompTIA Security+

    35 hours · beginner

    • Threat management
    • Vulnerabilities
    • Incident response
  2. Start before this

    CompTIA CySA+

    30 hours · intermediate

    • Threat detection
    • Incident response
    • Security tools
  3. Start before this

    CompTIA PenTest+

    30 hours · intermediate

    • Penetration testing
    • Vulnerability assessment
    • Reporting
  4. Start before this

    CEH v13

    40 hours · intermediate

    • Ethical hacking
    • Reconnaissance
    • Web testing
  5. You are here

    CISSP

    50 hours · advanced

    • Security management
    • Risk
    • Architecture
  6. Next step

    Splunk SIEM

    30 hours · advanced

    • Log analysis
    • SIEM
    • Threat hunting
Ready to start with CISSP Training - Certified Information Systems Security Professional?Try the free lab first, or review the fee and enroll in a few steps.

Connect the concepts.
Put them to work.

Move from understanding a system to configuring, testing and improving it through guided practice.

  • Configure a network

    Trace connections and practice working with devices and services.

  • Test what changes

    Explore lab scenarios and inspect how configuration choices affect a system.

  • Build repeatable workflows

    Explore Linux, scripting and automation in the relevant learning paths.

Explore the lab environments

Confirm the available labs and access period for your chosen course.
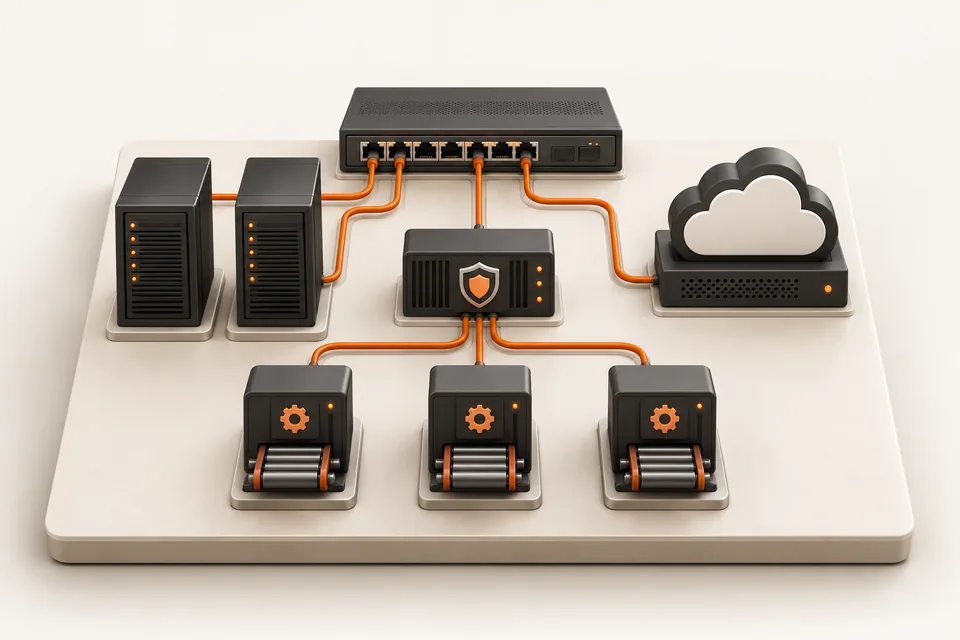
Illustration of a miniature switch, servers, cloud, security gateway and delivery modules connected in an infrastructure learning lab.
A connected view of networking, cloud, security and automation.

Learn from top 1% engineers.

Meet instructors who bring networking, cloud and automation experience into the classroom.

Atul Sharma
Founder · Networking

Atul Sharma

12+ years in networking

Networking experience spanning Aricent, TCS, Apple and Juniper.
Sanjay Sharma
AWS cloud

Sanjay Sharma

20+ years of experience

Cloud mentor bringing extensive hands-on AWS experience to the classroom.
Amit Bhatt
Linux & DevOps

Amit Bhatt

11+ years of experience

DevOps automation experience at CDAC, IBM and Integrated Solutions.

Industry experience. Practical explanations. A human connection.

Explore Network Kings
Aadil Hameed dar

Aadil Hameed dar

Network Engineer L1

“Industry-expert trainers made networking easy to understand.”

Shared with Network Kings

Explore, talk it through, or enroll.

See the syllabus and fees at your own pace. Request personal guidance when you need help choosing.

Find the right direction.

Discuss your experience, interests and the skills you want to build with our team.

Request career guidance

Have a course question?

Ask about prerequisites, live classes, lab access or the enrollment options for your course.

Request a callback

Ready for your next skill?

Compare our learning formats, then open your chosen course to review enrollment options.

Explore learning plans

Use the enquiry form to share your course interest, or WhatsApp/email to include a callback or guidance request.

Why learn from the top 1% of engineers?

Because passing an exam and doing the job are different skills, and only experience closes the gap. Network Kings mentors have spent 11 to 20+ years building and running networks, cloud platforms and pipelines at companies like Apple, Juniper Networks, IBM and CDAC. They teach what breaks in production, why, and how engineers fix it under pressure.
  • Atul Sharma, Founder & CEO
  • Sanjay Sharma, AWS
  • Vikas Kumar, Azure
  • Ajay, Azure
  • Amit Bhatt, Linux & DevOps
  • Lazaro (Laz) Diaz, Networking

Atul Sharma (Founder & CEO, 12+ yrs), Sanjay Sharma (AWS, 20+ yrs), Vikas Kumar (Azure, 20+ yrs) and more. Meet the mentors

Same problem, two answers. Pick a track:

On the job: The SIEM raises hundreds of alerts before lunch, and one of them is real.

The textbook answer

A SIEM collects logs and generates alerts. Analysts investigate each alert and escalate incidents.

Correct. Not enough to fix it.
How a production engineer teaches it

  1. Triage by asset value and attack stage, not by arrival time.
  2. Join the login, the process tree and the outbound connection into one story.
  3. Contain the host, then hand over a timeline the incident team can act on.
  4. Tune the noisy rule so tomorrow's queue is shorter than today's.
  • The why behind every command, not just the syntax.
  • Hands-on labs for every topic, so the first fault you fix is not at work.
  • Doubts answered by someone who has fixed it in a live network, cloud or pipeline.