Different Types of Hackers and the Networking Skills Behind Cybersecurity
Explore different types of hackers and learn how networking skills like TCP/IP, subnetting, protocols, routing, and traffic analysis support cybersecurity.
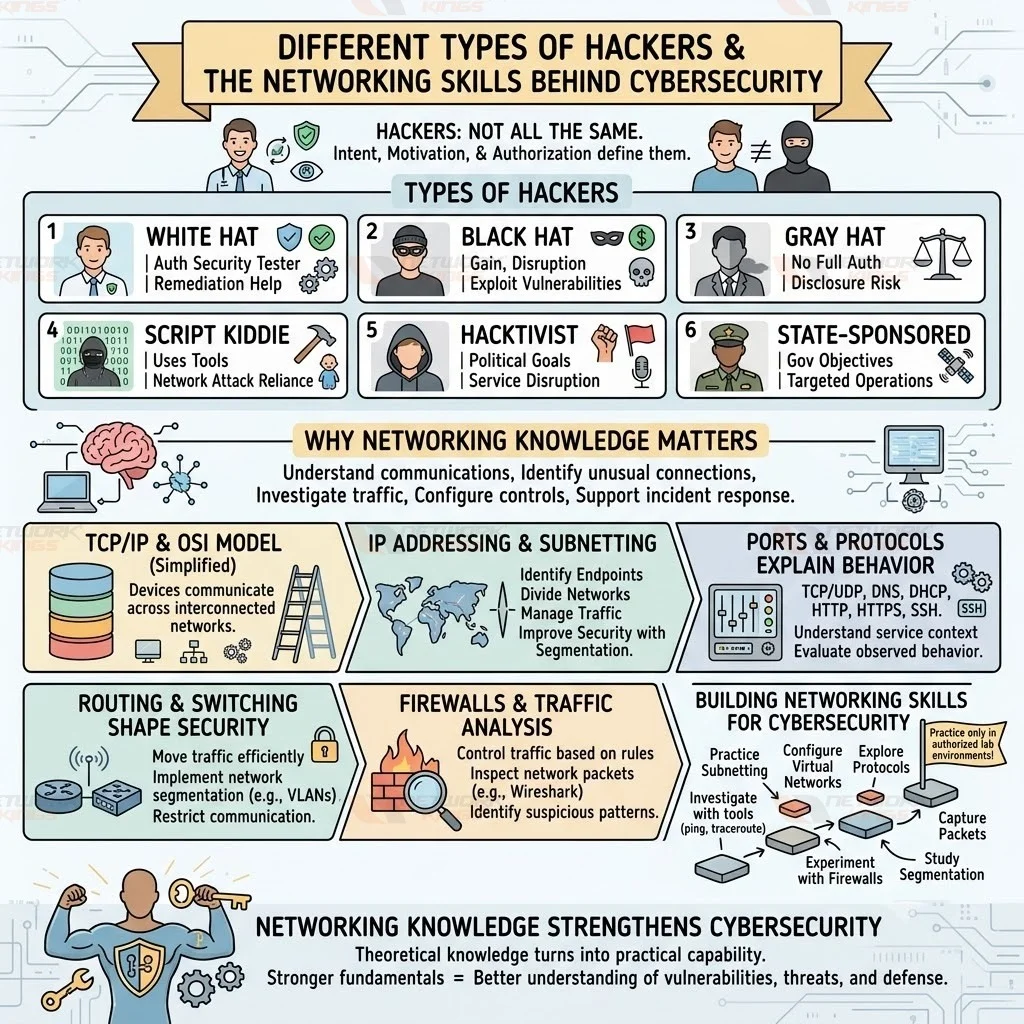
Not every hacker has the same intentions, methods, or legal status. Some are hired to find weaknesses before criminals exploit them. Others steal data, disrupt services, or target organizations for political or financial reasons. The difference often comes down to motivation, authorization, and objectives.
Understanding hacker categories is useful, but it is only part of learning cybersecurity. To recognize suspicious behavior and protect systems effectively, security professionals also need a strong grasp of computer networking. Attacks often move through networks, rely on exposed services, manipulate traffic, or exploit weaknesses in how devices communicate.
For anyone pursuing ethical hacking or cybersecurity, networking knowledge provides the technical foundation needed to understand these activities.
Understanding the different types of hackers
Hackers can be grouped into several categories based on their intentions and methods. These labels are useful for understanding cybersecurity roles and threats, although real-world activity does not always fit perfectly into one category.
Hacker type | Typical motivation | Networking relevance |
White hat hacker | Authorized security testing | Identifies and helps remediate network vulnerabilities |
Black hat hacker | Financial gain, disruption, or unauthorized access | Exploits weaknesses in systems and networks |
Gray hat hacker | Finds vulnerabilities without full authorization | May discover and disclose security weaknesses |
Script kiddie | Uses existing tools without deep technical knowledge | Often relies on pre-built network attack tools |
Hacktivist | Political or social objectives | May target websites, services, or network availability |
State-sponsored hacker | Government or strategic objectives | May conduct intelligence and targeted cyber operations |
Cybercriminal | Financial or criminal objectives | May target credentials, systems, data, or network services |
The distinction between these groups is important. For example, a white hat hacker may use penetration testing techniques to identify a weakness because they have permission to test the environment. A black hat hacker could attempt to exploit a similar weakness without authorization for personal or criminal gain.
Technical capability alone does not determine whether hacking activity is ethical. Authorization and intent matter.
Why networking knowledge matters in cybersecurity
Most modern security incidents involve communication between systems. An attacker may attempt to reach a vulnerable service, move between compromised systems, establish an external connection, or communicate with infrastructure controlled by an attacker.
A cybersecurity professional who understands networking can investigate these activities at a technical level.
Imagine an endpoint begins making repeated connections to an unfamiliar external address. Rather than simply labeling the activity as malicious, an analyst can examine the destination, protocol, port, frequency, and surrounding traffic to determine whether it is expected.
Networking knowledge is particularly valuable for:
Understanding how devices communicate
Identifying unusual network connections
Investigating suspicious traffic
Configuring security controls
Supporting incident response
Performing authorized penetration testing
Designing network segmentation
This is why networking is not just a separate IT skill. It directly supports cybersecurity analysis and defense.
TCP/IP and the OSI model
The TCP/IP model helps explain how devices communicate across interconnected networks. Cybersecurity professionals should understand how IP addresses identify endpoints and how TCP and UDP support different types of communication.
The OSI model provides another useful way to understand network behavior and troubleshoot problems. The value is not in memorizing seven layers for an exam. It is in recognizing where a problem may exist.
For example, if a user cannot reach an application, the issue could involve physical connectivity, switching, IP configuration, routing, DNS resolution, firewall rules, or the application itself. Thinking through these layers helps security and IT professionals narrow down the problem instead of making assumptions.
IP addressing and subnetting
IP addressing is fundamental to understanding network traffic. Security professionals need to know how devices are identified, how networks are divided, and how traffic moves between different subnets.
Important concepts include:
IPv4 and IPv6
Subnet masks
CIDR notation
Network and host addresses
Default gateways
Private and public IP addresses
Subnetting
Subnetting also has security implications. Organizations can separate users, servers, applications, and sensitive resources into different network segments. This can reduce unnecessary communication and help limit the potential impact of a compromised system.
Ports and protocols explain network behavior
When investigating network activity, knowing which protocol is being used can provide valuable context.
DNS translates domain names into IP addresses. DHCP provides devices with network configuration. TCP establishes reliable connections, while UDP provides connectionless communication. HTTP and HTTPS support web traffic, and SSH enables secure remote administration.
Cybersecurity professionals should understand protocols such as:
TCP and UDP
DNS and DHCP
HTTP and HTTPS
ARP
ICMP
SSH
You do not need to memorize every possible port number. It is more useful to understand what a service does, how it communicates, and whether the observed behavior makes sense for that environment.
Routing and switching shape network security
Routers and switches determine how traffic moves through a network. Switches connect devices within network segments, while routers connect different networks and make forwarding decisions.
Security professionals should understand MAC addresses, VLANs, trunking, routing tables, and network segmentation because these technologies influence which systems can communicate.
Consider a company that separates employee workstations, production servers, and sensitive databases into different VLANs. If one employee device is compromised, appropriate segmentation can restrict unnecessary communication with other systems. Segmentation does not eliminate risk, but it can reduce the potential reach of an incident.
Firewalls and network traffic analysis
Firewalls provide another important layer of network protection. They can control traffic based on addresses, ports, protocols, and other defined rules.
Understanding firewall behavior is useful when investigating both attacks and legitimate connectivity problems. For example, an unexpected connection could be blocked by a firewall, while a poorly configured rule could unintentionally expose a service.
Packet analysis provides even deeper visibility. Tools such as Wireshark allow security and networking professionals to inspect network packets and study communication between systems.
This can help identify unusual connections, unexpected protocols, repeated requests, or communication patterns that deserve further investigation.
Building networking skills for cybersecurity
Networking concepts become much easier to understand when they are practiced rather than memorized. Anyone preparing for an ethical hacking or cybersecurity career can build practical knowledge through controlled lab environments.
A useful learning path includes:
Practice IPv4 addressing and subnetting.
Build simple virtual networks.
Configure basic routing and switching scenarios.
Explore DNS, DHCP, TCP, and UDP behavior.
Practice troubleshooting with ping, traceroute, and nslookup.
Capture and examine network traffic with a packet analysis tool.
Experiment with firewall rules in an authorized lab.
Study how network segmentation affects communication.
The important point is to practice only in environments where you have explicit permission. Ethical hacking is based on authorized testing, controlled experimentation, and responsible handling of security findings.
Networking knowledge strengthens cybersecurity skills
Knowing the different types of hackers provides useful context, but understanding networking explains what happens technically when systems communicate.
A strong cybersecurity foundation should therefore include TCP/IP, IP addressing, subnetting, protocols, routing, switching, VLANs, firewalls, and traffic analysis. These skills help professionals understand both normal network behavior and the signs that something may be wrong.
For aspiring ethical hackers, penetration testers, security analysts, and other cybersecurity professionals, networking should not be treated as a box to check before moving on to security.
The stronger your networking fundamentals, the easier it becomes to understand how vulnerabilities are exposed, how suspicious activity travels across an environment, and how defensive controls can reduce risk. That combination of networking knowledge and security thinking is what turns theoretical cybersecurity knowledge into practical technical capability.
FAQs
1. Why is networking knowledge important for ethical hackers?
Networking knowledge helps ethical hackers understand how systems communicate and where security weaknesses may exist. Concepts such as TCP/IP, ports, routing, DNS, VLANs, and network segmentation allow testers to assess how traffic moves through an environment and identify weaknesses within authorized testing boundaries.
2. How do hackers use network protocols during an attack?
Different attacks can involve different network protocols depending on the target and objective. Attackers may interact with DNS, HTTP/HTTPS, TCP, UDP, or other services exposed by a system. Understanding normal protocol behavior helps cybersecurity professionals recognize unusual connections, unexpected traffic patterns, or potentially compromised services.
3. How does subnetting contribute to network security?
Subnetting divides a larger IP network into smaller logical networks. When combined with appropriate access controls and segmentation, this can limit unnecessary communication between systems. For example, user devices, application servers, and sensitive databases can be placed into separate network segments to reduce the potential impact of a compromised endpoint.
4. What is the difference between network scanning and penetration testing?
Network scanning generally focuses on discovering hosts, services, ports, and other characteristics of a network. Penetration testing goes further by evaluating whether identified weaknesses can be meaningfully exploited within an authorized scope. Scanning can therefore be one component of a broader security assessment rather than a complete penetration test.
5. How can packet analysis help detect suspicious activity?
Packet analysis provides visibility into network communications. Security professionals can examine addresses, protocols, ports, packet patterns, and connection behavior to investigate potentially abnormal activity. Tools such as Wireshark can help analysts understand what is actually happening on the network instead of relying only on high-level alerts.
6. Why should cybersecurity professionals understand TCP and UDP?
TCP and UDP behave differently and support different communication requirements. TCP provides connection-oriented, reliable communication, while UDP does not establish a traditional connection and has lower protocol overhead. Understanding these differences helps professionals interpret network traffic and investigate services that use either transport protocol.
7. How do VLANs and network segmentation help defend against hackers?
VLANs can logically separate devices and network traffic, while broader segmentation strategies can control communication between different network zones. Properly configured segmentation can make lateral movement more difficult by limiting which systems can communicate directly. It should be combined with access controls, monitoring, and other security measures rather than treated as a standalone defense.
8. Can someone learn ethical hacking without strong networking skills?
It is possible to begin learning ethical hacking without an advanced networking background, but strong networking fundamentals become increasingly important as the subject becomes more technical. Understanding IP addressing, protocols, ports, routing, switching, DNS, and network traffic makes it easier to understand vulnerabilities and troubleshoot security issues effectively.