MPLS Explained: How Multiprotocol Label Switching Works
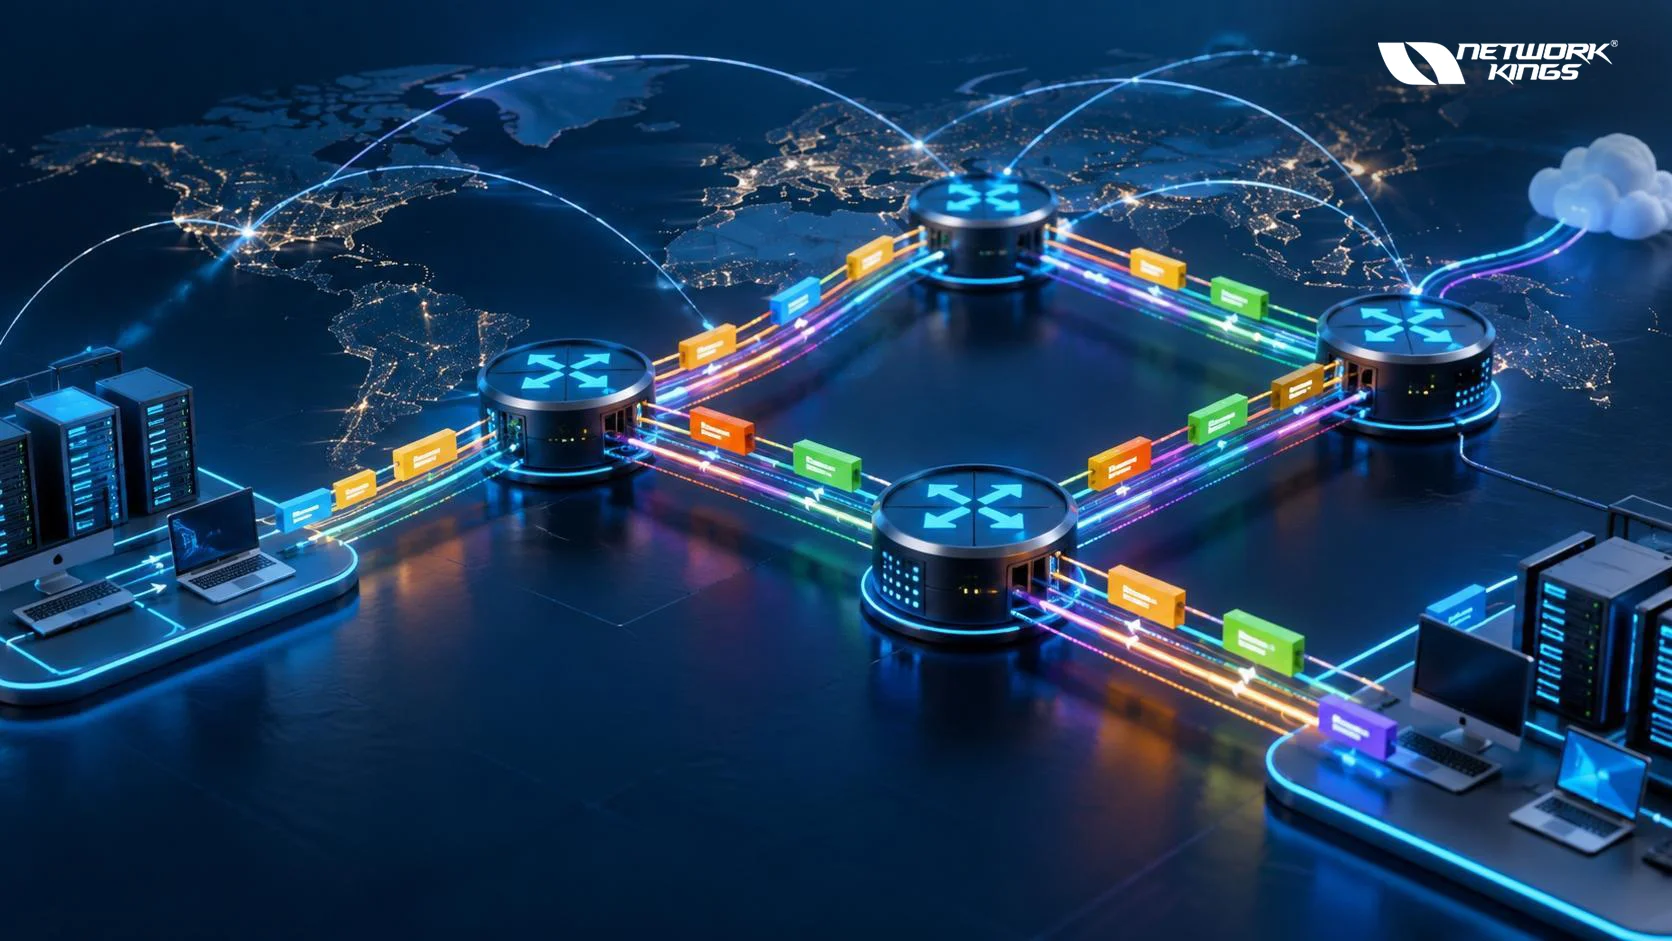
MPLS, short for Multiprotocol Label Switching, is a forwarding technique that moves packets across a network using short labels instead of a full IP routing lookup at every hop. A router at the network edge attaches a label to each packet, and the routers in the core forward it based on that label alone.
That small change gives service providers and large enterprises things plain IP routing does not offer easily: predictable paths, traffic engineering, and clean separation between customers on shared infrastructure. This guide covers how MPLS works, how a packet moves through it, and where it fits in modern networks.
What Is MPLS
MPLS is a protocol-independent packet forwarding mechanism that operates between Layer 2 and Layer 3. The label is inserted between the data link header and the IP header, so MPLS is often called a Layer 2.5 technology. It can carry IPv4, IPv6, and Layer 2 frames such as Ethernet, which explains the word "multiprotocol."
In short, MPLS classifies traffic once at the network edge, attaches a label, and forwards the packet along a defined path through the network.
Why MPLS Was Introduced
In the 1990s, many providers ran IP over ATM and Frame Relay cores, and software-based IP lookups were a performance concern. MPLS grew out of earlier tag switching efforts to combine the simplicity of IP routing with the speed and path control of connection-oriented technologies.
Hardware-based IP forwarding later erased most of the raw speed argument. What kept MPLS valuable was control. Operators could steer traffic, build VPNs, and run several services over one shared core.
How MPLS Works
MPLS has a control plane and a data plane. The control plane uses an IP routing protocol such as OSPF or IS-IS to learn the topology, then a label distribution mechanism assigns labels to destinations. The data plane forwards packets using those labels.
The process follows three stages. The ingress router classifies the packet and pushes a label. Routers in the core forward the packet by looking up the label and swapping it. The egress side removes the label and delivers the packet using normal IP forwarding.

Understanding MPLS Labels
An MPLS label is a 20-bit value that tells a router which forwarding entry applies to the packet. It sits inside a 32-bit MPLS header with four fields:
Label, 20 bits, the value used for the forwarding lookup
Traffic Class, 3 bits, used for quality of service marking
Bottom of Stack, 1 bit, set on the last label in a stack
TTL, 8 bits, which works like the IP time to live
Labels have local significance. Each router chooses the label values it expects to receive, so a label is only meaningful between two neighboring routers. Packets can also carry a stack of labels, which is how MPLS VPNs and traffic engineering tunnels are built.
LER, LSR and LSP Explained
A Label Edge Router (LER) sits at the boundary of the MPLS network. The ingress LER pushes the label, and the egress LER removes it. A Label Switch Router (LSR) sits in the middle and forwards packets purely by label swapping.
A Label Switched Path (LSP) is the one-way path a labeled packet follows from ingress to egress. Because LSPs are unidirectional, return traffic uses a separate LSP.
Labels become attached to traffic through a Forwarding Equivalence Class (FEC), a group of packets that receive the same forwarding treatment, such as all traffic destined for a particular prefix. The Label Distribution Protocol (LDP) lets neighboring routers advertise which label they will use for each FEC. Other mechanisms exist, including RSVP-TE for explicit paths and BGP for VPN labels, but LDP is the most common way to build basic LSPs.
How a Packet Travels Through an MPLS Network
Imagine a branch office at 10.1.1.10 sending traffic to a server at 192.168.20.5 across a provider network. The path is PE1, P1, P2, then PE2. PE1 and PE2 are LERs, and P1 and P2 are LSRs.
The packet arrives at PE1 as a normal IP packet. PE1 performs a lookup, matches the destination to an FEC, and pushes label 100.
P1 receives the packet and checks only the label. Its table says to swap 100 for 200 and send the packet to P2. P1 never examines the IP header.
P2 is the penultimate router. By default, it removes the label (penultimate hop popping) and forwards the plain IP packet to PE2. This saves PE2 an extra lookup.
PE2, the egress router, performs a normal IP lookup and delivers the packet toward the server.
Intermediate routers make one simple decision label in and label out. The path was fixed when the LSP was established, not recalculated hop by hop.
MPLS vs Traditional IP Routing
Feature | Traditional IP Routing | MPLS |
Forwarding method | Each router does a longest prefix match on the destination IP address | Core routers forward using an exact match on the label |
Primary decision | Made independently at every hop from the routing table | Made at the ingress when traffic is assigned to a FEC |
Traffic path | Follows the IGP or BGP best path unless policy overrides it | Follows an LSP, which can match the IGP path or an engineered path |
Scalability | Core routers may need to carry wide routing information | Customer routes can stay at the edge while the core carries only provider routes |
Common use cases | General internet and LAN routing | Provider backbones, private WANs, VPN services, traffic engineering |
MPLS does not replace IP routing. It depends on an IGP to build the topology, so the two work together.
Where MPLS Is Used
MPLS is especially common where organizations need predictable WAN connectivity across multiple locations.
Typical applications include:
Enterprise WAN connectivity
Service-provider backbone networks
Layer 3 VPN services
Layer 2 VPN services
Quality-of-service implementations
Traffic engineering
Connecting geographically distributed branches
MPLS VPN architectures can allow multiple customers or organizations to share provider infrastructure while maintaining separate routing contexts.
MPLS VPN Explained
One of the most important practical uses of MPLS is VPN connectivity.
In a typical Layer 3 MPLS VPN architecture, customer edge devices connect to provider edge routers. The PE routers maintain separate routing information for different customers, commonly using VRFs. MP-BGP can distribute VPN routing information between PE routers, while MPLS labels help transport the traffic across the provider backbone.
This allows many customer networks to use the same provider infrastructure without requiring each customer to build a separate physical backbone.
Advantages and Limitations of MPLS
MPLS provides several useful capabilities, particularly for large WAN environments:
Scalable VPN services
Controlled traffic forwarding
Traffic engineering capabilities
Support for QoS
Separation of customer routing information
Integration with established routing architectures
However, MPLS is not automatically the best choice for every organization. It depends on provider availability, architecture, operational requirements, cost, and application needs. Modern organizations may also evaluate Internet-based connectivity and SD-WAN alongside MPLS.
Is MPLS Still Relevant
Yes, but its role has shifted. Service providers still rely on MPLS in their backbones, and many enterprise networks still use provider MPLS services. At the same time, many organizations now combine MPLS with internet links or use SD-WAN to reduce dependence on a single transport. Whether MPLS is the right choice depends on application requirements, geography, and budget, not on a universal rule.
Conclusion
MPLS forwards traffic by labels assigned at the network edge, using LSPs built with LDP and related protocols. Its lasting value lies in path control, VPN services, and operational flexibility, which is why it remains a core technology even as WAN designs evolve.
FAQs
What is MPLS in networking?
MPLS is a forwarding method in which routers use short labels, rather than IP lookups at every hop, to move packets along predefined paths. It is widely used in provider backbones and private WAN services.
How does MPLS work?
The ingress router assigns a label to the packet, core routers swap labels as the packet moves along an LSP, and the egress side removes the label and forwards the IP packet normally.
What is an MPLS label?
It is a 20-bit value in a 32-bit MPLS header that identifies the forwarding entry for a packet. Labels are only locally significant between neighboring routers.
What is the difference between MPLS and IP routing?
IP routing makes an independent destination-based decision at every hop. MPLS classifies traffic at the edge and forwards it along a label path. MPLS still relies on IP routing protocols to build the network topology.
Is MPLS still used today?
Yes. Many service providers use it in their cores, and many enterprises still buy MPLS services, often alongside internet connectivity or SD-WAN.
The founder of Network Kings, is a renowned Network Engineer with over 12 years of experience at top IT companies like TCS, Aricent, Apple, and Juniper Networks. Starting his journey through a YouTube channel in 2013, he has inspired thousands of students worldwide to build successful careers in networking and IT. His passion for teaching and simplifying complex technologies makes him one of the most admired mentors in the industry.